
Data Governance: The Foundation of Secure, Compliant, and Intelligent Business Operations
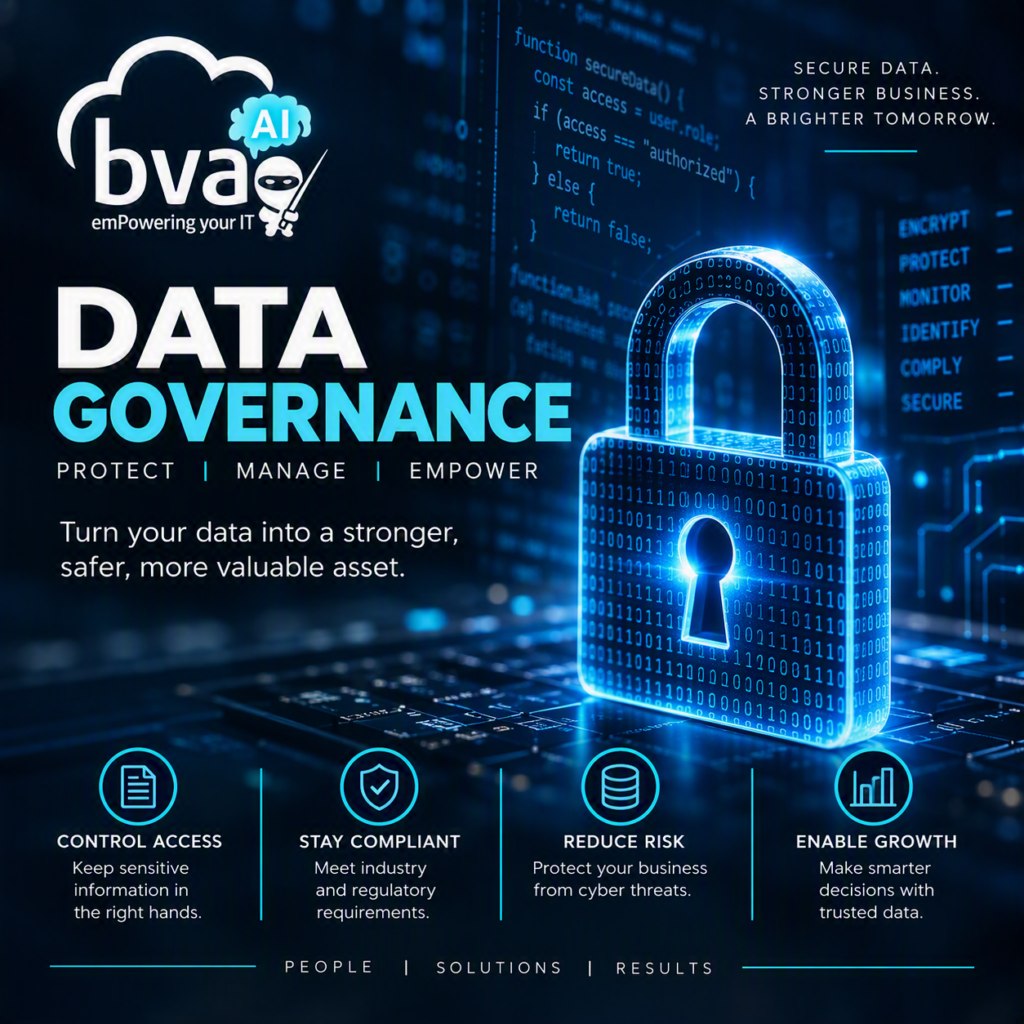
Today’s organizations generate and store more data than ever before. From customer records and employee information to financial documents and operational data, information has become one of the most valuable assets a business owns.
However, collecting data without a strategy for managing it creates significant risks. Data sprawl, unauthorized access, compliance violations, inaccurate reporting, and cybersecurity threats can quickly turn valuable information into a liability.
This is where Data Governance becomes essential.
What is Data Governance?
Data governance is the framework of policies, processes, and controls that determines:
- Who owns data
- How data is classified
- Who can access it
- How it is stored and protected
- How it is monitored and audited
- How long it is retained
- When and how it is securely disposed of
Simply put, data governance establishes the rules for managing information across your organization.
Without governance, businesses often struggle with disconnected systems, inconsistent information, security vulnerabilities, and growing compliance risks.
Data Governance vs. Data Security
Many organizations mistakenly believe data governance and cybersecurity are the same thing. While closely related, they serve different purposes.
Data Governance Defines the Rules
Examples include:
- Assigning ownership of business data
- Categorizing information by sensitivity
- Defining retention policies
- Establishing compliance requirements
- Determining access permissions
Data Security Enforces the Rules
Examples include:
- Multi-factor authentication (MFA)
- Endpoint protection
- Encryption
- Security monitoring
- Threat detection and response
- Backup and disaster recovery
Think of data governance as the rulebook and cybersecurity as the enforcement team. Successful organizations need both working together.
The Core Components of an Effective Data Governance Program
1. Data Ownership and Accountability
Every critical business dataset should have a designated owner responsible for:
- Accuracy
- Integrity
- Compliance
- Access approvals
- Lifecycle management
When ownership is clearly defined, accountability improves across the organization.
2. Data Classification
Not all information carries the same level of risk.
Organizations should classify data into categories such as:
- Public
- Internal Use
- Confidential
- Restricted
Classification helps ensure sensitive information receives appropriate protection and handling.
3. Least-Privilege Access Controls
Employees should only have access to the information necessary for their role.
Benefits include:
- Reduced insider risks
- Smaller attack surfaces
- Improved compliance
- Easier auditing and oversight
Maintaining least-privilege access becomes especially important as organizations grow and employees change roles.
4. Audit Logging and Monitoring
Organizations should maintain a record of:
- Data access
- Changes made
- Data transfers
- Permission changes
- Security events
Complete audit trails provide visibility, improve investigations, and support compliance requirements.
5. Data Retention and Lifecycle Management
Keeping data indefinitely creates unnecessary risk.
A governance program should establish:
- Retention schedules
- Archiving policies
- Regulatory requirements
- Secure disposal procedures
Proper lifecycle management reduces storage costs and minimizes exposure to outdated or unnecessary data.
Why Data Governance Matters Across Every Industry
While compliance requirements vary by sector, every business benefits from stronger control over its information.
Healthcare
Protect patient information while supporting HIPAA compliance requirements.
Professional Services
Secure client records, contracts, and confidential communications.
Manufacturing
Protect intellectual property, production data, and vendor information.
Construction
Maintain project documentation, financial records, and employee data securely.
Legal Firms
Control access to privileged and confidential client information.
Retail and E-Commerce
Protect customer data and payment information while improving operational reporting.
Nonprofits
Manage donor records and financial information responsibly while maintaining trust.
Financial Services
Support regulatory compliance and protect highly sensitive financial information.
Regardless of industry, organizations face the same fundamental challenge: ensuring information remains accurate, accessible to authorized users, and secure from unauthorized access.
Common Data Governance Challenges
Many small and midsized organizations face similar obstacles:
Data Silos
Information lives in multiple systems that do not communicate effectively.
Legacy Technology
Older systems often lack modern access controls, auditing capabilities, and security features.
Shadow IT
Employees may store data in unauthorized applications, cloud storage platforms, or personal devices.
Resource Constraints
Most organizations do not have dedicated data governance teams or Chief Data Officers.
Rapid AI Adoption
Artificial Intelligence tools introduce new concerns regarding data privacy, ownership, and information sharing.
Without visibility into where data resides and how it is being used, organizations significantly increase their operational and security risks.
Data Governance in the Age of AI
The rapid growth of AI applications has created new governance requirements.
Organizations should establish clear policies surrounding:
- Approved AI tools
- Permitted business use cases
- Sensitive information restrictions
- Employee training
- AI activity monitoring
- Data sharing limitations
Employees may inadvertently expose confidential information by entering sensitive business data into public AI platforms without understanding the risks.
A strong governance framework helps organizations safely embrace innovation while protecting valuable information assets.
Building a Practical Data Governance Strategy
Organizations don’t need a large compliance department or a Chief Data Officer to improve data governance.
A practical roadmap includes:
Step 1: Identify and Inventory Data
Understand where business-critical and sensitive information resides.
Step 2: Classify Information
Categorize data based on sensitivity and business impact.
Step 3: Assign Ownership
Define accountability for key systems and datasets.
Step 4: Implement Access Controls
Follow the principle of least privilege.
Step 5: Enable Logging and Monitoring
Track activity and monitor for anomalies.
Step 6: Define Retention Policies
Establish clear guidelines for storing and disposing of information.
Step 7: Review and Improve
Governance should evolve alongside your business, technology, and regulatory landscape.
How BVA Technology Services Can Help
At BVA Technology Services, we help organizations establish governance frameworks that align security, compliance, and operational efficiency.
Our team can assist with:
- Microsoft 365 Data Governance
- Data Classification and Labeling
- Data Loss Prevention (DLP)
- Identity and Access Management
- Multi-Factor Authentication
- Cybersecurity Risk Assessments
- Backup and Disaster Recovery Planning
- Compliance Readiness Reviews
- AI Governance Strategies
- Security Monitoring and Incident Response
Whether you’re managing hundreds of employees or a small growing business, a strong data governance foundation helps protect your organization while enabling smarter decision-making and sustainable growth.
Summation
Data is one of your organization’s most valuable assets, but only when it is properly managed and protected.
Data governance creates the structure that allows businesses to secure information, meet compliance requirements, reduce cyber risk, and confidently leverage emerging technologies like AI.
Organizations that treat data as a strategic asset today will be better positioned to compete, innovate, and grow tomorrow.